
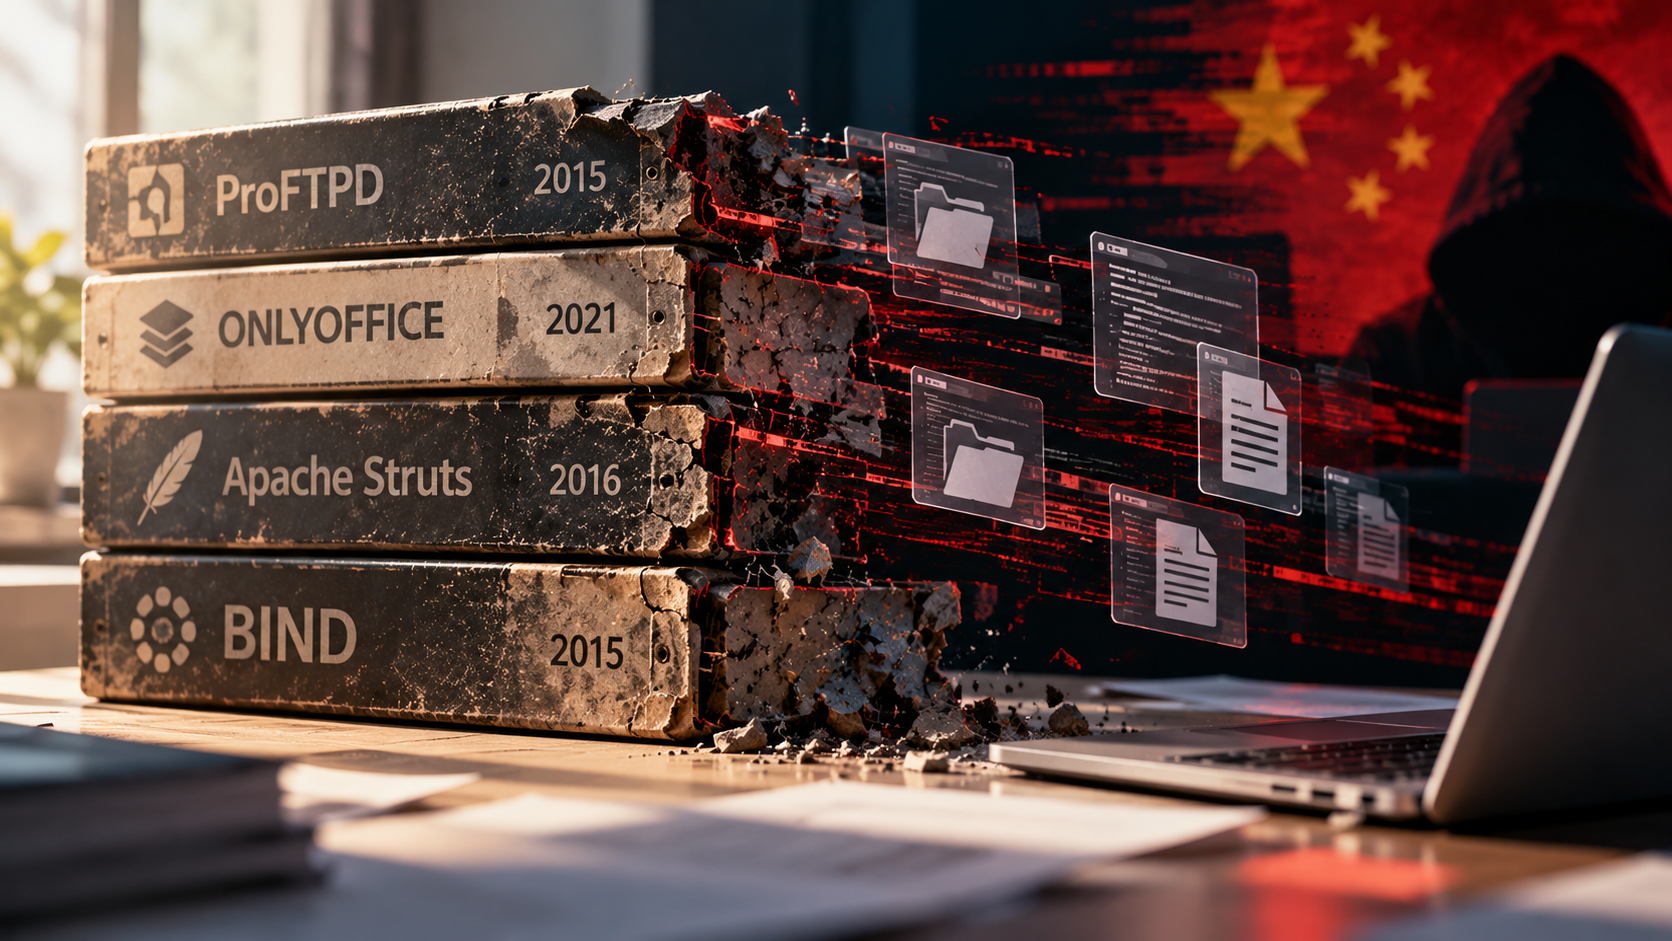
On October 9, 2026, the US cybersecurity agency CISA added five vulnerabilities to its catalog of Known Exploited Vulnerabilities (KEV). The oldest of them are more than ten years old. Fixes have existed for a long time, but attackers still successfully hit systems that nobody updated. In other words, outdated software becomes the easiest target for them.
The attacks are linked to the Chinese group Flax Typhoon. A joint advisory from the intelligence services of seven countries (the US, the UK, Australia, Canada, Japan, New Zealand and Spain) links it to the Beijing company Integrity Technology Group, which works for the Chinese government.
Which vulnerabilities entered the catalog
- ProFTPD, CVE-2015-3306 (CVSS 10.0). The FTP server lets anyone copy files without authentication, for example to drop a malicious script into the website folder.
- ONLYOFFICE Document Server, CVE-2021-3199 (CVSS 9.8). An image upload lets an attacker leave the allowed folder and potentially run code on the server.
- Apache Struts, CVE-2016-3081 (CVSS 8.1). Command injection in web applications built on this framework.
- ISC BIND, CVE-2015-5477 (CVSS 7.5). A specially crafted query crashes the DNS server.
- Strapi, CVE-2023-22894 (CVSS 7.2). An admin panel user can extract password hashes and password reset tokens.
CISA ordered US federal agencies to fix these flaws by October 11. For other organizations this deadline is not mandatory, but the agency urges them to update first as well.
How Flax Typhoon works
- Mass scanning. The Microscan tool, which the FBI and the US Justice Department recently seized, contained more than 1,300 ready-made exploits.
- A botnet of cameras and routers. In 2024, the FBI took down the group’s botnet of more than 260,000 routers, surveillance cameras and network storage devices worldwide.
- Password guessing for email. The attackers brute-forced Exchange and Microsoft 365 accounts and then gained a foothold through VPN.
- Targets: energy companies, airports (including in Poland), gas operators, universities and international organizations.
Outdated software: why it concerns Ukrainian organizations
The main lesson is simple: the most dangerous flaw is not a new one but an old one that everyone forgot. A server that someone set up and left “because it works” stays open for years. Moreover, attacker scanners find such systems automatically.
Government bodies, local authorities and critical infrastructure are especially vulnerable. They often run old servers, internal portals and document systems that nobody has inventoried for years. Besides, SSSCIP already checks compliance under a new state control methodology. So outdated software is not only an attack risk but also a reason for an order to fix violations.
Read also: Cisco releases a critical firewall update; Hackers attack Cisco email gateways through attachments; The SSSCIP list of banned technologies reaches 880 items.
How S-byte can help you close old flaws in outdated software
- Information security audit and vulnerability assessment. We inventory servers, services and software and find outdated versions and resources exposed to the internet.
- Building information security systems (ISS). We set up a vulnerability and update management process so that old systems do not drop out of sight.
- Technical support with SLA. We track the CISA KEV catalog and vendor advisories and update systems on time.
- Account protection. Multi-factor authentication from RSA Security makes password guessing useless. S-byte has already confirmed TPI compliance of RSA ID Plus E3.
- Secure video surveillance. We install cameras with proper security settings, updated firmware and a separate network segment, so they do not become part of someone’s botnet.
Do you know how many outdated systems run in your network? Contact S-byte, and we will carry out an inventory and vulnerability assessment.